TIBBIR Universe · Saved post receipt · 1881719341848076621
MEMELORDENKI
@MemeLordEnki · Published: Tue Jan 21 15:03:46 +0000 2025
Original post on X · Full data receipt · Backup index
Saved archive render, not a screenshot of the original X page. Full captured content is retained below; capture gaps are stated explicitly. Video files are not stored.
I don’t believe it’s too smart to wait for a “formal confirmation” here
All of the proofs and “coincidences” that are linked to $TIBBIR is close to impossible to fake.
Unless they managed to
1. Steal Micky Malka’s wallet
2. Hack another 13 wallets that belong to a co-founder of @RibbitCapital, top employees, Investors, other VC’s that have connections to Ribbit.
3. Force Micky Malka to create a trust called “TIBBIR TRUST” and send 100,000 Robinhood shares to it, few weeks before launching $TIBBIR
I also think it’s very unlikely that a VC who has over a decade in the industry, personal contacts to the founders of leading AI companies like OpenAI, and it investing billions of dollars into development of Crypto/AI would be dumb enough to launch a simple shill bot. Setting up a trust is kind of a pain in the ass, i’m not sure if I would set one up “only for a shill bot”.
VC’s were the first ones to hear about DEFAI. They’ve been here before us, before it catched momentum.
“I get that it’s them, but why does it take so much time for them for make a confirmation??”
Great question, cause i’m sure they wouldn’t do a stealth launch. 😶🌫️
Day by day we have more and more coincidences happening.
🤷♂️I have zero fucking clue🤷♂️nfa🤷♂️
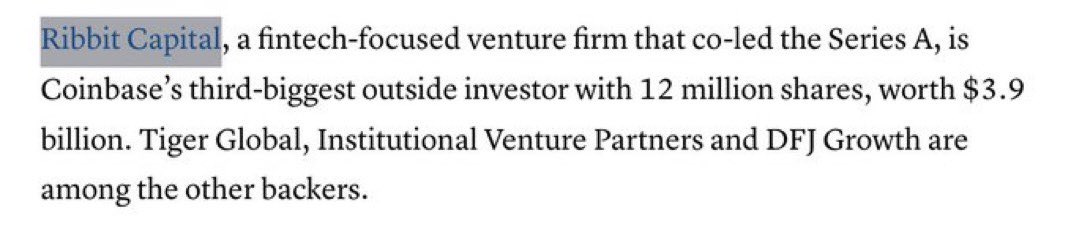
Image source: https://pbs.twimg.com/media/Gh01xIHWAAES4uq.jpg?name=orig
Image source: https://pbs.twimg.com/profile_images/2106342603180404736/-jo7Qu5D_200x200.jpg
Posts that embed this post
Provenance and integrity
{
  "path": "sources/community-deep-dive-2026-10-14/fx-1881833023836152031.json",
  "sha256": "f8943cfbc0e9d7a246e2c52e43f944b14a4ab1df1aceda05bd2c09aafa8c2557",
  "retrieved_at": null
}
Receipt generated: 2026-10-15T09:54:52.894331+00:00. Publication and retrieval dates are separate. SHA-256 hashes detect changes; they do not independently authenticate the publisher.