TIBBIR Universe · Saved post receipt · 1955676079655362577
MopHandle
@MopHandel · Published: Wed Aug 13 17:01:26 +0000 2025
Original post on X · Full data receipt · Backup index
Saved archive render, not a screenshot of the original X page. Full captured content is retained below; capture gaps are stated explicitly. Video files are not stored.
"""""Disclaimer******* - This is AI compiled opinion of the IMAGINED $TIBBIR vision stack.
Agentic Finance Stack — TIBBIR‑Centric One‑Pager
TL;DR: Decagon converts messy human rules (contracts, policies, workflows) into machine‑readable artifacts; TIBBIR verifies those artifacts (KYA/“Reg‑OK”, permits, badges) so agents can act under guardrails; custody/policy rails (e.g., Fireblocks/MPC) execute; payments rails (e.g., Razorpay/Lightspark) settle; an attestation/audit layer closes the loop.
Example Flow (Intent → Verified Action → Audit)
Policy ingestion: Treasury rules/SLAs/docs → Decagon parses & mints permits/attestations/context tokens.
Agent scopes: Enterprise binds agent with ERC‑4337 session keys + scoped approvals (spend limits, counterparties, time windows).
Verification: Counterparty checks TIBBIR (KYA/Reg‑OK credential, permits, reputation SBTs; no revocation present).
Execution: Fireblocks policy engine approves; MPC signs; transaction settles via Razorpay/Lightspark (or on‑chain DEX/bank rails).
Audit/feedback: Action + proof logged to EAS/attestation registry; violations trigger revocation; policies/tokens updated.
Key Artifacts (Machine‑Readable “LEGO”)
Identity/KYA: reusable verification (e.g., “Reg‑OK” credential, issuer‑signed).
Capability/Permit tokens: what an agent may do (limits, scopes, roles).
Context tokens: preferences/constraints (risk, vendor lists, time windows).
Session keys (4337): time‑boxed, revocable authorizations bound to accounts.
Reputation SBTs: non‑transferable track records for agents/issuers.
Revocation lists: immediate kill‑switch for compromised scopes/agents.
Why This Matters
From talk → action: Agents don’t just “see”; they act with provable permissions.
Compliance by construction: Policies encoded as tokens + policy engines → audit trails by default.
Composability & scale: Standardized credentials enable cross‑platform, multi‑agent workflows.
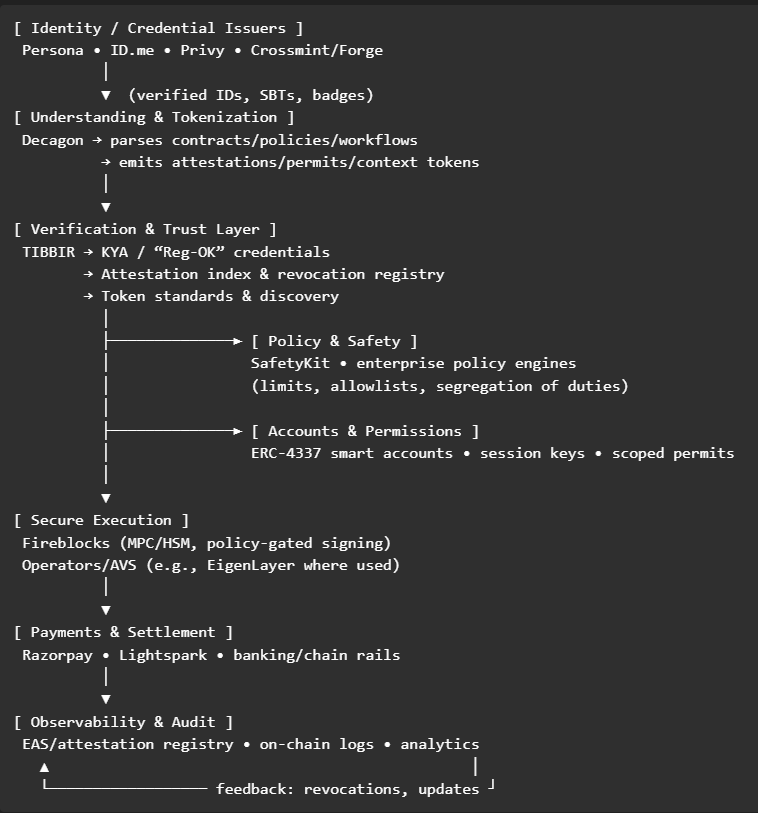
Image source: https://pbs.twimg.com/media/GyPys5VXAAAWjWh.png?name=orig
Image source: https://pbs.twimg.com/profile_images/1982914236595527680/3PAKBt0g_200x200.jpg
Quoted and embedded posts — separate backups
Provenance and integrity
{
  "path": "sources/community-deep-dive-2026-10-14/fx-1955676079655362577.json",
  "sha256": "8db78116ac9efdbb96fbcdeb65257d53a32b2e77d988371ca5d83af5a14e9c53",
  "retrieved_at": null
}
Receipt generated: 2026-10-15T09:54:53.766240+00:00. Publication and retrieval dates are separate. SHA-256 hashes detect changes; they do not independently authenticate the publisher.